TDT4237: Software Security
Introduction
This subject does not have a book, and is made up of different resources. It's mostly based around the OWASP Testing Guide - a book which is a part of the curriculum. Also, a huge part of the Security Engineering by Ross Anderson is a part of the curriculum. This compendium is therefore based around those books, a whole section to each where the idea is to provide a summary of each chapter/section of these books.
There's also a few articles that's a part of the curriculum. The idea is to provide a summary of the whole article, but if someone has the time, it may be a good idea to provide a summary of the different sections of the major ones.
As for the OWASP Testing Guide, it's possible to fill more out in chapter 4. That chapter is about actual tests. I who wrote the first draft of this compendium didn't think those would be very relevant for an exam, but only for the project. You may be asked to suggest tests on an exam, so it may be a good idea for someone to go through that and write a summary.
Curriculum
The curriculum as of fall 2015 is the following:
- OWASP Test Guide v4.0 - the entire book
- Ross Anderson, Security Engineering, second edition Ch. 1-5 (Chaper 5, only pages 129-160) and 8-9
- The Risk Management Framework
- Software Security Touchpoints
- The Trustworthy Computing Security Development Lifecycle
- Threat Modeling - part 6.1 in the SHIELDS document
- IEEE: Demystifying the threat modeling process
- OpenSAMM pages 3-16(Executive Summary + Understanding the model):
- Security requirements in the cloud, report by SINTEF
- The Common Criteria ISO/IEC 15408
All the lecture slides are also part of the curriculum!
How to pass
- Learn the RMF and Threat Modeling processes
- Read over your old exercises to get tips on technical risks, attacks etc. Also read or look through the OWASP Testing Guide for inspiration.
- Read through these notes
If you manage to give some answer on the RMF and Threat Modeling tasks, and also have some knowledge about the theoretical questions, you should be more than good to go.
The Three Pillars of Software Security
The three main aspects when working with software security are the following:
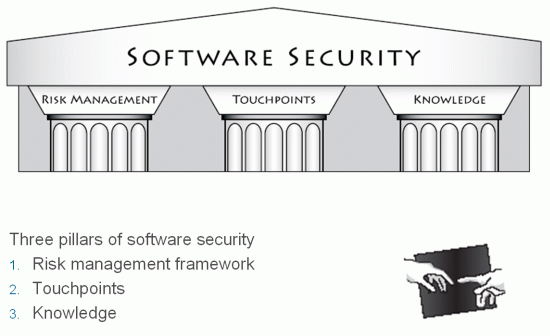
- How to identify and manage risks in your software (described later on)
- Software Security Touchpoints, a set of best practices to improve security (also described later on)
- Knowledge about security, e.g. known threats, what works and what doesn't (can't really be described in ONE document)
OWASP Top 10
OWASP Top 10 lists the 10 most dangerous threats according to the OWASP organization. It was last updated in 2017, but our list below is based on the 2013 version, which you can find here.
The updated 2017 list is available here.
The following is a table describing each of the 10 items shortly. The descriptions are copied from the OWASP top 10 overview page.
| Number | Name | Description |
| A1 | Injection | Injection flaws, such as SQL, OS, and LDAP injection occur when untrusted data is sent to an interpreter as part of a command or query. The attacker’s hostile data can trick the interpreter into executing unintended commands or accessing data without proper authorization. |
| A2 | Broken Authentication and Session Management | Application functions related to authentication and session management are often not implemented correctly, allowing attackers to compromise passwords, keys, or session tokens, or to exploit other implementation flaws to assume other users’ identities. |
| A3 | Cross-site scripting (XSS) | XSS flaws occur whenever an application takes untrusted data and sends it to a web browser without proper validation or escaping. XSS allows attackers to execute scripts in the victim’s browser which can hijack user sessions, deface web sites, or redirect the user to malicious sites. |
| A4 | Insecure Direct Object References | A direct object reference occurs when a developer exposes a reference to an internal implementation object, such as a file, directory, or database key. Without an access control check or other protection, attackers can manipulate these references to access unauthorized data. |
| A5 | Security Misconfiguration | Good security requires having a secure configuration defined and deployed for the application, frameworks, application server, web server, database server, and platform. Secure settings should be defined, implemented, and maintained, as defaults are often insecure. Additionally, software should be kept up to date. |
| A6 | Sensitive Data Exposure | Many web applications do not properly protect sensitive data, such as credit cards, tax IDs, and authentication credentials. Attackers may steal or modify such weakly protected data to conduct credit card fraud, identity theft, or other crimes. Sensitive data deserves extra protection such as encryption at rest or in transit, as well as special precautions when exchanged with the browser. |
| A7 | Missing Function Level Access Control | Most web applications verify function level access rights before making that functionality visible in the UI. However, applications need to perform the same access control checks on the server when each function is accessed. If requests are not verified, attackers will be able to forge requests in order to access functionality without proper authorization. |
| A8 | Cross-Site Request Forgery (CSRF) | A CSRF attack forces a logged-on victim’s browser to send a forged HTTP request, including the victim’s session cookie and any other automatically included authentication information, to a vulnerable web application. This allows the attacker to force the victim’s browser to generate requests the vulnerable application thinks are legitimate requests from the victim. |
| A9 | Using Components with Known Vulnerabilities | Components, such as libraries, frameworks, and other software modules, almost always run with full privileges. If a vulnerable component is exploited, such an attack can facilitate serious data loss or server takeover. Applications using components with known vulnerabilities may undermine application defenses and enable a range of possible attacks and impacts. |
| A10 | Unvalidated Redirects and Forwards | Web applications frequently redirect and forward users to other pages and websites, and use untrusted data to determine the destination pages. Without proper validation, attackers can redirect victims to phishing or malware sites, or use forwards to access unauthorized pages. |
The OWASP Testing Guide
Chapter 1: Testing Guide Frontispiece
Presents some contributors, revision history, how to contact OWASP-contributors etc.
Chapter 2: The OWASP Testing Project
Principles of Testing
- There is no silver bullet
- Think strategically, not tactically
- The SDLC is King
- Test early and often
- Understand the scope of security
- Develop the right mindset
- Understand the Subject
- Use the right tools
- The Devil is in the Details
- Use Source Code When Available
- Develop metrics
- Document the test results

Testing Teqhniques Explained
Manual inspections & reviews
Human reviews that typically test the security implications of people, policies and process. Include inspection of technology decisions. Interviews and review of documentation.
Advantages:
- Requires no supporting technology
- Can be applied to a variety of situations
- Flexible
- Promotes teamwork
- Early in the SDLC
Disadvantages:
- Can be time consuming
- Supporting material not always available
- Requires significant human thought and skill to be effective
Threat Modeling
Develop a model, and use that in the design of the software to stop threats. Developed as early as possible in the SDLC.
Use a simple approach to develop the threat model. The OWASP Guide recommends the NIST 800-30 standard for risk assessment.
That approach involves (from the book):
- Decomposing the application – use a process of manual inspection to understand how the application works, its assets, functionality, and connectivity.
- Defining and classifying the assets – classify the assets into tangible and intangible assets and rank them according to business importance.
- Exploring potential vulnerabilities - whether technical, operational, or management.
- Exploring potential threats – develop a realistic view of potential attack vectors from an attacker’s perspective, by using threat scenarios and attack trees
- Creating mitigation strategies - develop migitating controls for each of the threts deemded to be realistic
Outputs a collection of lists and diagram.
Advantages:
- Practical attacker’s view of the system
- Flexible
- Early in the SDLC
Disadvantages:
- Relatively new technique
- Good threat models don’t automatically mean good software
Code Review
Modeling and analysis cannot detect all errors. Code review is to go straight to the source code and look for security vulnerabilities. There's no substitute for code review/looking at the source code when looking for vulnerabilities in web applications. Removes the guess work of black box testing.
Advantages:
- Completeness and effectiveness
- Accuracy
- Fast (for competent reviewers)
Disadvantages:
- Requires highly skilled security developers
- Can miss issues in compiled libraries
- Cannot detect run-time errors easily
- The source code actually deployed might differ from the one being analyzed
Penetration Testing
Penetration testing has been in use for many years. Also known as black box testing or ethical hacking. The point is to run the application remotely to try to find security vulnerabilites, without knowing the inner workings of the application. The tester acts as an attacker.
Advantages:
- Can be fast (and therefore cheap)
- Requires a relatively lower skill-set compared to source code review
- Tests the code that is actually being exposed
Disadvantages:
- Too late in the SDLC
- Front impact testing only
A balanced approah
You need to combine the methods. The book presents examples where one method alone does not find all security vulnerabilities.


Deriving Security Test Requirements
You'll need testing objectives to have successful testing. Testing objectives are specified in security requirements.
Deriving functional and non-functional test requirements
Functional Security Requirements
Requirements that state expected functionality that can be validated through security tests, are referred to as 'positive requirements'.
Example of high-level security design requirements for authentication (examples of positive requirements):
- Protect user credentials and shared secrets in transit and in storage
- Mask any confidential data in display (e.g., passwords, accounts)
- Lock the user account after a certain number of failed log in attempts
- Do not show specific validation errors to the user as a result of a failed log on
- Only allow passwords that are alphanumeric, include special characters and six characters minimum length, to limit the attack surface
- Allow for password change functionality only to authenticated users by validating the old password, the new password, and the user answer to the challenge question, to prevent brute forcing of a password via password change.
- The password reset form should validate the user’s username and the user’s registered email before sending the temporary password to the user via email. The temporary password issued should be a one time password. A link to the password reset web page will be sent to the user. The password reset web page should validate the user temporary password, the new password, as well as the user answer to the challenge question.
Risk driven security requirements
'Negative requirements' are requirements that validate the application for unexpected behavior. Negative requirements can be difficult to test, as there is no expected behavior to look out for.
Example:
- The application should not allow for the data to be altered or destroyed
- The application should not be compromised or misused for unauthorized financial transactions by a malicious user.
Use cases are used to develop functional requirements for an application. Misues and abuse cases describes unintended and malicious use scenarios of the applications. These can be used to further develop requirements.
To derive security requirements from use and misuse cases, you can follow this step-by-step methodology:
- Describe the functional scenario
- Describe the negative scenario
- Describe functional and negative scenarios with use and misuse case
- Elicit the security requirements.
This figure shows graphical representation of the example from the guide:

Security Tests Integrated in Development and Testing Workflows
During development the developers should validate and analyze source code, write unit tests and use tools to help find potential vulernabilites.
There should also be security tests as a part of integration tests. These should include white box, black box and grey box tests.
Security Test Data Analysis and Reporting
The metrics used should be well thought out before one starts the testing phase. One also has to decide what level the application should be at when it comes to security. This could mean setting an upper bound for security vulnerabilities, or how it should be compared to other applications. There should be a clear goal with the testing phase, e.g. reduce the number of vulnerabilities to some number.
Data that should be included in a test report:
- The categorization of each vulnerability by type
- The security threat that the issue is exposed to
- The root cause of security issues (e.g., security bugs, security flaw)
- The testing technique used to find the issue
- The remediation of the vulnerability (e.g., the countermeasure)
- The severity rating of the vulnerability (High, Medium, Low and/ or CVSS score)
You can present business cases to show that the security test metrics provides value to the organization's security test data stakeholders, e.g. managers, developers, information security offices, auditors etc.
Chapter 3: The OWASP Testing Framework
Describes a typical testing framework that can be developed within an organization. Can be seen as a references framework that comprises techniques and tasks that are appropriate at various phases of the SDLC. -The OWASP Testing Guide
The framework presented is not focused on any specific development methodology. It's based around the activities that are to take place:
- Before development begins
- During definition and design
- During development
- During deployment
- Maintenance and operations
Phase 1: Before Development Begins
Phase 1.1 - Define a SDLC: You must define the SDLC, where security must be a part of each stage.
Phase 1.2 - Review Policies and Standards: Then you must review standards and policies, as you must know what they are to be able to follow them. Without guidelines, you cannot base yourself on the work done by other experts.
Phase 1.3 - Develop Measurements and metrics Criteria and Ensure Traceability: The process may need modification to be able to capture the data you want, so it's essential that this is done before the complete process starts.
Phase 2: During Definition and Design
Phase 2.1 - Review Security Requirements: First review security requirements, which define how the application should work from a security perspective. The requirements has to be tested. When looking for gaps in the requirements, it's smart to look at security mechanisms such as:
- User Management
- Authentication
- Authorization
- Data Confidentiality
- Integrity
- Accountability
- Session Management
- Transport Security
- Tiered System Segregation
- Legislative and standards compliance (including Privacy, Government and Industry standards)
Phase 2.2 - Review Design and Architecture: Then move on to look at the architecture and the design, and review the documents associated with that. This includes models, textual documents and similar artifacts. To find security flaws in the design/architecture is the most cost-effective, and it's also the place where changes are most effective. E.g. if authorization has to be made more than one place in the system, consider creating a authorization component.
Phase 2.3 - Create and Review UML Models: Create and review UML models, so that the system designers have an exact understanding of how the application works.
Phase 2.4 - Create and Review Threat Models: Move on to create and review threat models, based on the design and archutectural reviews, and the UML diagrams. Design realistic threat scenarios, and analyze the design and architeture to see that these threats have been mitigated, accepted by the business or assigned to a third party (e.g. a insurance firm).
Revisit design if a threat doesn't have a mitigation strategy.
Phase 3: During Development
In theory there shouldn't be any need for phases or strategies in this development, as the development is the implementation of the design. If the design is well thought out, all possible threats have already been mitigated. In practice, that's not the case. Implementation can drift away from design. You can have human errors in implementation, or the design can be faulty. The developer will face many decisions, that can and will affect the security of the application.
Phase 3.1 - Code Walk Through: The security team should do a code walk through with the developers, and in some cases the system architect. This is a high-level walk though. The developers explain the logic and flow of the implementation. This gives the code review team a general understanding of the code. The purpose is not code review, but understand the high level structure of the application.
Phase 3.2 - Code Review: When there's a good understanding of the flow and structure of the application.
These code reviews validate the code against a static checklist, that includes the following:
- Business requirements for availability, confidentiality, and integrity.
- OWASP Guide or Top 10 Checklists for technical exposures (depending on the depth of the review).
- Specific issues relating to the language or framework in use, such as the Scarlet paper for PHP or Microsoft Secure Coding checklists for ASP.NET.
- Any industry specific requirements, such as Sarbanes-Oxley 404, COPPA, ISO/IEC 27002, APRA, HIPAA, Visa Merchant guidelines, or other regulatory regimes.
The return on investment (time invested), these code reviews has extremely high quality return compared to alternatives, and rely the least on the skill of the reviewer.
Phase 4: During Deployment
Phase 4.1 - Application Penetration Testing: A last check to see that nothing has been missed in design or implementation.
Phase 4.2 - Configuration Management testing: Even though the application itself can be safe, the infrastructure and configuration of the deployment should also be tested.
Phase 5: Maintenance and Operations
Phase 5.1 - Conduct Operational Management Reviews: You need to document how the application and infrastructure is managed, and have a process surrounding it.
Phase 5.2 - Conduct Periodic Health Checks: Either monthly or quarterly health checks should be performed on the application as well as the infrastructure to ensure that no new threats has somehow been introduced.
Phase 5.3 - Ensure Change Verification: Changes has to be tested by QA in a QA environment, but also tested in the deployment environment to ensure that the level of security is not affected by the change.

Chapter 4: Web Application Security Testing
Describes the 12 subcategories of the Web Application Penetration Testing Methodology.
What is web application security testing? A security test is a way of methodically evaluating a computer system or network with regards to security. It can verify effectiveness of application security controls, or network security controls.
| Term | Explanation |
| Vulnerability | A flaw or weakness in the system's design, implementation, operation or management. This could be exploited, and used to compromise the security of the system. |
| Threat | Anything (user, system instability, external software) that can harm the assets of an application by exploiting a vulnerability. |
| Test | An action to demonstrate that a system or application meets the requirements of the stakeholders. |
What is the OWASP Testing Methodology? A collected list of known black box testing techniques. The model consists of a tester, tools and methodology and the application to test. It's divided into two phases: Passive mode and active mode.
| Mode | Description |
| Passive | The tester tries to understand the application's logic, and plays with it. This is a information gathering phase, and tools can be used to assist in the process. At the end of the phase, all access points/end points of the application should be known and understood, e.g. HTTP URLs, headers, cookies, methods etc. |
| Active | The phase where the tester actually is testing the application. There are 11 subcategories for a total of 91 controls. The test guide describes these. |
Testing for Information Gathering
- Conduct search engine discovery/reconnaissance for information leakage
- Search with
site:yourwebsite.comin different search engines - Look at the Google Hacking database to help build searches
- The goal is the see if there is any leaked sensitive information
- Search with
- Fingerprint Web Server
- Find out what type of web server it is allows the penetration tester to exploit known vulnerabilites in the software
- Can be done with Netcat or simply
curlthe URL and look at the headers. Note that there are many ways to obfusate or modifiy the server banner string. - One can also look at the ordering of the headers returned, e.g. Apache and IIS has different orderings. The test guide provides different examples
- Another way to detect the server software is to send a malformed request, e.g. request non-existent pages. The responses will be different for the different server softwares. The test guide provides examples. These things can also vary with the version of the server. Also note that the differences can be shown by sending invalid HTTP methods/ requests.
- Automated testing, e.g. with Httprint. or an online service like the OWASP Unmaskme Project.
- Review Webserver Metafiles of Information Leakage
- Involves testing the
robots.txtfile for information leakage. The file describes accepted behavior of Web Spiders, Robots and Crawlers. E.g. allowed user-agents, and disallowed directories. A crawler/spider/robot can intentionally ignore arobots.txt-file. - A
robots.txt-file can be analysed using Google Webmaster Tools
- Involves testing the
- Enumerate Applications on Webserver
- There are usually more than one application running on a server today, or more than one application associated with a public IP.
- Is tested with black box tests
- Issues/factors when testing:
- Apps can be placed under different subdirectories, e.g.
example.com/app1andexample.com/app2. These can be referenced by other web pages and found through those. You can also use scanners. The web server may be misconfigured and let you browse the directories, and you may suddenly find some of the applications. You can also probe URLs that are likely to hold an application, e.g.mail.example.com,example.com/webmailetc. - Most webapps lie on port
80or443(HTTP and HTTPS), but apps can run on other ports. Can be easily solved with a port scanner, e.g.nmap, for instancenmap –PN –sT –sV –p0-65535 192.168.1.100, which will run a TCP connect scan and look up all ports on the IP192.168.1.100, and try to determine which services are running on those ports. - Multiple virtual machines can run under a domain. You'll need to find out which DNS names are associated with an IP-address.
- Determining the DNS name server, and query them for zone transfers. This may return additional DNS
- DNS inverse queries: Set record type to PTR and issue an IP request
- Web-based DNS searches
- Reverse IP-services
- Googling
- Review webpage comments and metadata for information leakage: Developers use comments to save information, and some info may not have been removed before putting the application into production. Look at HTML and JS code (black box testing) by opening the code view from your browser.
- Meta tags can help profile the webapp
- Meta tags can also be used by the developer to alter HTTP response headers. See if these can be used to conduct an attack, e.g. CLRF
- Identify application entry points
...
Chapter 5: Reporting
Performing the technical side of the assessment is only half of the overall assessment process. The final product is the production of a well written informative report. A report should be easy to understand, and should highlight all the risks found during the assessment phase. -The OWASP Testing Guide
The report needs three major sections. The sections should be independent of each other, so that each section can be printed out and given to the appropriate team.
Executive summary
The exec summary sums up overall findings of the research. This is meant for the business managers and system owners, and should give a high level view of the vulnerabilities that has been discovered. The executives won't have time to read the whole thing, so they want answers to the questions "What's wrong?" and "How do we fix it?". These questions should be answered in one page.
Test Parameters
Intro to this chapter should outline parameters of the security testing.
The OWASP Testing guide gives the following suggested headings:
- Project objective: Objective and expected outcome
- Project scope
- Project schedule
- Targets: Lists the applications and systems that are targeted.
- Limitations: Outlines all limitations that were encountered, e.g. in regards to methods or certain types of tests.
- Summary of the findings: Outline vulnerabilites
- Remediation Summary: Outline an action plan for fixing the vulnerabilities.
Findings
Gives detailed technical information about the vulnerabilites that were found, and the actions needed to solve them. The section is aimed at technical people, so include everything. The section should include:
- Screenshot and commands that indicate what tasks was done
- Affected item
- Technical description of the issue and what it affects
- Section on how to resolve the issue
- A severity rating
Security Engineering
Based on Ross Anderson's book 'Security Engineering', second edition.
The book can be found here
Chapter 1: What is Security Engineering?
1.1: Introduction
The conventional view is that while software engineering is about ensuring that certain things happen (‘John can read this file’), security is about ensuring that they don’t (‘The Chinese government can’t read this file’).
1.2: A Framework
Good security engineering requires four things:
- Policy: What you are to achieve
- Mechanism: Ciphers, access control, hardware, controls, machinery ..
- Assurance: Reliance on a particular mechanism
- Incentive: Motive that guardians of a system do their job properly, and the motive that the attackers have to defeat your policy
1.3 to 1.6: Examples of systems
Read them if you want.
1.7: Definitions
Most of these definitions are from the book.
Definitions when talking about a system. In practice, the term system can denote:
- a product or component, such as a cryptographic protocol, a smartcard or the hardware of a PC;
- a collection of the above plus an operating system, communications and other things that go to make up an organization’s infrastructure;
- the above plus one or more applications (media player, browser, word processor, accounts / payroll package, and so on);
- any or all of the above plus IT staff;
- any or all of the above plus internal users and management;
- any or all of the above plus customers and other external users.
Important terms in relation to security:
| Term | Definition |
| Vulnerability | A flaw or weakness in the system's design, implementation, operation or management. This could be exploited, and used to compromise the security of the system. |
| Threat | Anything (user, system instability, external software) that can harm the assets of an application by exploiting a vulnerability. |
| Security failure | When a threat exploits a vulnerability. |
| Security policy | Statement of a system's protection strategy. |
| Security target | Detailed specification that describes how and by which means a security policy will be implemented in a product. |
Other words and terms:
| Word or term | Definition |
| Subject | A physical person |
| Person | A physical (human) or legal person (organization/company) |
| Principal | An entity that participates in a security system |
| Secrecy | The effect of the mechanisms used to limit the number of principals who can access information, such as cryptography or computer access controls |
| Confidentiality | Obligation to protect some other person's or organization's secrets if you know them |
| Privacy | The ability to protect your personal information, and extends to the ability to prevent invasions of your personal space. Can also be a a right. |
| Protection | A property such as confidentiality or integrity, defined in a sufficiently abstract way for us to reason about it in the context of general systems rather than specific implementations. |
There are more mentioned, e.g. the difference between trust and trustworthy is explained with an example with the NSA.
1.8 Summary
There's some confusion about the terms in use in the security engineering community. Computer security can be a lot of things, and many things, e.g. social interactions, are related. A robust security design requires protection goals to be explicit.
Chapter 2: Usability and Psychology
2.1 Introduction
As technology has advanced, social/psychological attacks to computer systems are the greatest threat to online security, see for example phishing.
2.2 Attacks Based on Psychology
| Attack | Description |
| Pretexting | The act of creating and using a invented scenario - a pretext - to build trust and make the target reveal sensitive information. E.g. calling from a fake doctors office to 'confirm'(in other words retrieve) a social security number. |
| Phishing | Sending an e-mail that looks official that demands that the target reveals some sensitive information. Usually the e-mail states some consequences if the information is not handed over. E.g. a phishing e-mail can look like it comes from a bank, and state that the bank account of the target will be closed unless the target confirms his or her social security number, or gives some password/PIN etc. to confirm is identity, and that the account isn't used for illegitimate purposes. |
2.3 Insights from Psychology Research
2.3.1 What the brain does worse than the computer
There are many different human errors the security engineer should be aware of.
There's been and still is a lot of research on human error in regards to computer systems.
Types of errors:
- Capture errors: When an action has been done many times, it becomes practices. Through inattention you can repeat the practices action, even though you intended to do something else.
- Post-completion error: When you've completed your immediate goal, you are easily distracted from tidying-up actions, e.g. removing your bank card after a ATM withdrawal.
- Actions made based on rules are open to errors when the rules are wrong: A phishermen can make a target use the site by having the site use HTTPS, and starting URLs with the bank name.
- Mistakes done by people due to cognitive reasons - they simply don't understand the problem. IE7 had a anti-phishing toolbar that didn't stop phishing, because the team developing it didn't completely understand the problem.
2.3.2 Perceptual Bias and Behavioral Economics
Really just a page and a half with some introductory knowledge on behavioral economics. It mentions a few fields, and relates them to some facts about the human mind.
Wisdom from this section:
- We dislike losing 100 dollars more than we like the prospect of winning 100 dollars.
- Easily remembered data have more weight in mental processing
- We worry too much about unlikely events
- We have a constant underlying misconception about risk
- We are more afraid to lose something we have, than not making a gain of equivalent value
- We are more likely to go for something that's 'good enough', rather than work for something that's perfect: Most people go for the default system setup, as it wil be 'good enough'. This is a reason why security defaults matter.
2.3.3 Different Aspects of Mental Processing
- The mind is usually seen as one part 'cognitive' and one part 'affective'
- Fundamental attribution error: People often err trying to explain things with intentionality rather than situation.
- Teaching possible victims about the gory details of the Internet, e.g. by telling them to parse URLs that are sent in an email that seemingly comes from a bank, will be of limited value if the user's get bewildered
- Use security defaults, e.g. 'This bank does not send you emails' - remove the emotional element for the user
- Affect heuristic
- By first asking an emotional question, you can get the user to answer the subsequent questions with their heart more than their head
- Can be related to everything from risky behavior on porn sites to the use of celebrities in marketing
- Cognitive overload also increases reliance on affect
2.3.4 Differences Between People
- Men and women experience and use UIs differently
- There's been quite the amount of research on how women uses websites
- Most software today is made mostly by men
- It's not difficult to believe that the trend we're seeing in design of UIs and products may also be relevant when it comes to security engineering
2.3.5 Social Psychology
The growth of social-networking systems will lead to peer pressure being used as a tool for deception. There are many examples of abuse of authority, peer pressure and pretexting from the real world, that we as engineers can learn from.
2.3.6 What the Brain Does Better Than the Computer
Humans are better at recognizing humans visually, and image recognition generally.
2.4 Passwords
There are basically three options for authentication users to a system:
- Retain physical control of the device ('Something you have')
- Present something you know, e.g. a password ('Something you know')
- Use something like a fingerprint or iris scanner ('Something you are')
Most systems use the second option due to cost.
There are other things than passwords, that aren't obviously passwords, that can be used for the same purpose as the password. E.g. your mother's maiden name or a social security number. The first one is an example of a 'security question', and aren't that hard to guess if you know the name of the person you are trying to guess it for, so that you can research him or her. This has given the rise for the industry identity theft.
There are three broad concerns when it comes to passwords:
- Will the user enter the password correctly with a high enough probability?
- Will the user remember the password, or will they have to either write it down or choose one that’s easy for the attacker to guess?
- Will the user break the system security by disclosing the password to a third party, whether accidentally, on purpose, or as a result of deception?
The following sections describes different problems and challenges with passwords and users.
2.4.1 Difficulties with a Reliable Password Entry
A password can be too long and complex, which means that the user has difficulties entering it correctly. An urgent action protected by a password that's hard to enter, will have security implications.
2.4.2 Difficulties with Remembering the Password
Passwords can be hard to remember, which is a security risk. The problems related to remembering a password can be broken down to : Naive password choice, user abilities and training, design errors and operational failures.|
2.4.3 Naive Password Choice
To be able to remember their password, people choose words, names of their spouses or children, which is not that hard to find out. They also use complete words, which can be looked up in dictionaries. Engineers implemented password length requirements, and looked up password in dictionaries to see that it wasn't too easy but password quality enforcement is more complicated than that. After the rule that read 'at least six characters and at least one nonletters', Unix Secuirty reported that they built a file of the 20 most common female names plus a single digits, and tried them on several dozens machines. Of the 200 passwords, at least one was in use on the machines they tried. Daniel Klein ran a study where he gathered 25 000 encrypted Unix passwords and ran cracking software to break them, found that 21-25 % of the passwords could be guessed.
The requirement to change passwords regularly tends to backfire: Studies show that users either change the password until the password history is exhausted and they can use the password they want, or if it's a time limit on how often they can change it, they don't do it until an administrator helps them.
People are getting better at writing passwords, this shows the passwords retrieved from phishing sites. The most common password today isn't 'password', which it was before, but 'password1'.
2.4.4 User Abilities and Training
One can do a lot to protect passwords in e.g. a military or e-commerce environment, but you don't want to drive your customers away, and you can't order soldiers to do something they simply cannot do.
The author didn't find many relevant research articles on this, so he conducted an experiment himself, on first year computer science students. He asked three groups to create passwords after different rules. The conclusions he drew was:
- For users who follow instructions, passwords based on mnemonic phrases offer the best of both worlds. They are as easy to remember as naively selected passwords, and as hard to guess as random passwords.
- The problem then becomes one of user compliance. A significant number of users (perhaps a third of them) just don’t do what they’re told.
| Section | Description |
| 2.4.4.1 Design Errors | Don't ask for 'your mother's maiden name'. It's easy for a thief to find out, and it's based on an assumption that doesn't hold for all cultures. There are too many systems and applications today that ask for a password that's unique. It's too many passwords for the human mind to be able to remember. |
| 2.4.4.2 Operational Issues | Numbers or passwords to development or live systems lying around. Does not separate production and development environments completely. Failure to change default passwords. |
2.4.5 Social-Engineering Attacks
The biggest practical threat to passwords today, is that the user breaks the system security by giving the password to a third party, either willingly or as a result of deception. When it comes to deception, phishing (password fishing) has become a real problem.
2.4.6 Trusted Path
A trusted path refers to some means of being sure that you're logging into the system you think you're logging into, and that no one is eavesdropping. Instead of impersonating a police man to get a target's PIN, you place a false ATM in a shopping mall.
Skimmers are devices fitted over the front of real cash machines. These copy the card's data, and use a small camera to get the PIN.
2.4.7 Phishing Countermeasures
A large number of phishing countermeasures have been tried and proposed.
| Measure | Description |
| Password Manglers | Browser plugins that take the password the user entered and transparently turn it into a strong password, that only that website uses. The user can enter the same password everywhere, but each website has its own password. If the user uses his password on a phishing site, the site doesn't really get the real password. The solution is not very practical. |
| Client Certs or Specialist Apps | The SSL protocol supports certificates for the client and the server. The certificates are meant to identify its holder to the other principals in the transaction. A server cert can identify the website to your browser (lock icon). Client certs can make the authentication go both ways. Problem here is that certification systems are hard to manage, and JavaScript can be used to fool the browser. |
| Using the Browser's Password Database | Practical. The browser can ensure that it's the right URL, and can generate secure passwords. Problem is that the passwords may be saved unencrypted. To use this or not, depends on what you think is the greatest risk of keyloggers and phishing. Websites can make the browser unable to autofill websites with autocomplete="off" |
| Soft Keyboards | On-screen keyboards. Compromised by recording 40 pixels around each mouse click. |
| Customer Education | E.g. tell them to 'check the English', 'look for the lock symbol', 'check URLs' etc. The phishermen just worked around these advice, e.g. getting someone who speaks good English to write the e-mails. After a while the advice becomes too complex, and the countermeasure counterintuitive. It confuses users. |
| Microsoft Passport | Microsoft Passport is an old system for using Microsoft's logon facilities to authenticate the users of any merchant website. A user could his or hers login info from e.g. Hotmail, and get authenticated. The problem is that putting all your eggs in one basket, gives the people who want to steal and destroy eggs, a big incentive to kick that basket over. There were also a lot of technical flaws with the Microsoft Passport solution. Participating websites had to use Microsoft's web servers rather than free options such as Apache. There was also a fear that Microsoft's access to the mass of merchant data would extend their dominant position in the browser world, and also extend their monopoly. The login systems of Facebook and Google are based on the same idea: Single sign-on across the web. |
| Phishing Alert Toolbars | A toolbar that tells the user that the website he/she is visiting is a known phishing site. The phishers simply did a picture-in-picture attack to work around this: It displays a picture of a browser with a green toolbar in the gram of the normal browser. This is a UI problem that could be fixed, but even then the heuristic used to spot the dodgy sites has problems. Testing has to be dynamic, for instance. The toolbar would have to check each site visited, which is a privacy issue. |
| Two-factor Authentication | Great technology, but not completly implemented by small banks. There isn't enough pressure on some of the bigger banks at the time the book was written. Today this is used almost everywhere. The technology is described in chapter 3 under 'challenge-response' protocols. A problem could be that it's fiddly and time consuming to follow the protocol for each log on on every website. |
| Trusted Computing | 'TPM' chip on motherboards that can support functions as those of a CAP-device (see chapter 3, challenge-response. In short it's a device that can generate some value that can be used for log in, like those small 'calculators' we used with the bank before.). Having this on the motherboard, means that you can have bank transactions integrated in the computer. Roaming will be a problem. |
| Fortified Password Protocols | Merritt and Bellovin came in 1992 up with several authentication protocols where a guessable password could be used. Some people think that these can make a dent in the phishing industry when their patents run out, and they become a standard. |
| Two-channel Authentication | Involves sending an access code to the user via a seperate channel, e.g. a mobile phone. The problem is that attackers can do a 'man-in-the-middle'-attack (see chapter 3), just as they can with two-way authentication (challenge-response). |
For banking, two-channel authentication seems to give the most bang for the buck.
2.4.8 The Future of Phishing
It's hard to predict the future, but the author does it anyway.
2.5 System Issues
The fastest growing concern when it comes to passwords is phishing, and it's done most research on the pshychology related to passwords. That being said, there are some technical challenges too.
2.5.1 Can You Deny Service?
If you have some restriction that three wrong attempts closes off the account, won't a attack that floods the service with wrong login attempts bring down the service? What if this happens to a military system, right before an attack? No one can enter the systems, and everyone needs to be reactivated by an admin.
2.5.2 Protecting Oneself Or Others?
Make sure that if a user is hacked, that user cannot get the information of any other users.
2.5.3 Attacks on Password Entry
Password entry is usually badly protected.
| Attack | Description |
| Interface Design | Placement of physical PIN/password-entry console. Not censoring (that is setting input field type to password on the web) the password as it is written. |
| Eavesdropping | Free wifi on public spots, then eavesdrop on connections that aren't encrypted. A hotel manager can abuse the switchboard facilities, and track which buttons you press on the phone in your room. Many corporations still sends passwords and other sensitive information unencrypted over local networks |
| Technical Defeats of Password Retry Counters | Implementation details matter: How you implement password retry counters can become a vulnerability. |
2.5.4 Attacks on Password Storage
Passwords are often vulnerable when they are stored. You'll also need to protect login/registration logs.
| Issue | Description |
| One-way encryption | The password is through a one-way function that hashes it, based on some random salt, and the user logged in if it matches some pre-stored value. It is often implemented wrong. The right way is to generate a random salt, and save both the random hash and the salt |
| Password Cracking | It's still possible in some systems to guess a few thousands passwords, e.g. there is a tool that can guess 350 000 passwords each seconds to get into a Office-document. You can restrict guesses, e.g. WinZip limits you to 1000 guesses a second. The cracker software usually tries a dictionary word, then the word followed by some appendage, e.g. numbers. |
Chapter 3: Protocols
3.1: Introduction
What protocols are, and how they can fail.
3.2: Password Eavesdropping Risks
An example about how car unlockers in the 90's where too simple, as they used the serial number as the key for locking and unlocking.
3.3: Who Goes There? - Simple Authentication
Notation for protocols is shown with an example. The example is a car garage security mechanism, where the cars get's a key in the car when they enter. To open the bar when they leave, they have to beep the key. It then sends its serial number and then sends an authentication block consisting of the same serial number, followed by a random number, all encrypted using a key which is unique to the device.
Notation:
- The in-car token sends its name followed by the encrypted vlaue of
$T$ concatenated with$N$ , where$N$ is a number used once (aka nonce). It can mean anything that guarantees the freshness of a message. - Everything within the braces are encrypted.
- The
$N$ value's purpose is to assure the recipient that the message is fresh
Verification is simple:
- The parking garage server reds
$T$ , gets the corresponding key$KT$ , deciphers the rest of the message and checks that the nonce$N$ has not been seen before. - Finally checks that the plaintext contains
$T$
One reason many people get confused is that to the left of the colon, T identifies one of the principals (the token which represents the subscriber) whereas to the right it means the name (that is, the serial number) of the token. Another is that once we start discussing attacks on protocols, we can suddenly start finding that the token T’s message intended for the parking garage G was actually intercepted by the freeloader F and played back at some later time. [..] Professionals often think of the
$ T \rightarrow G$ to th